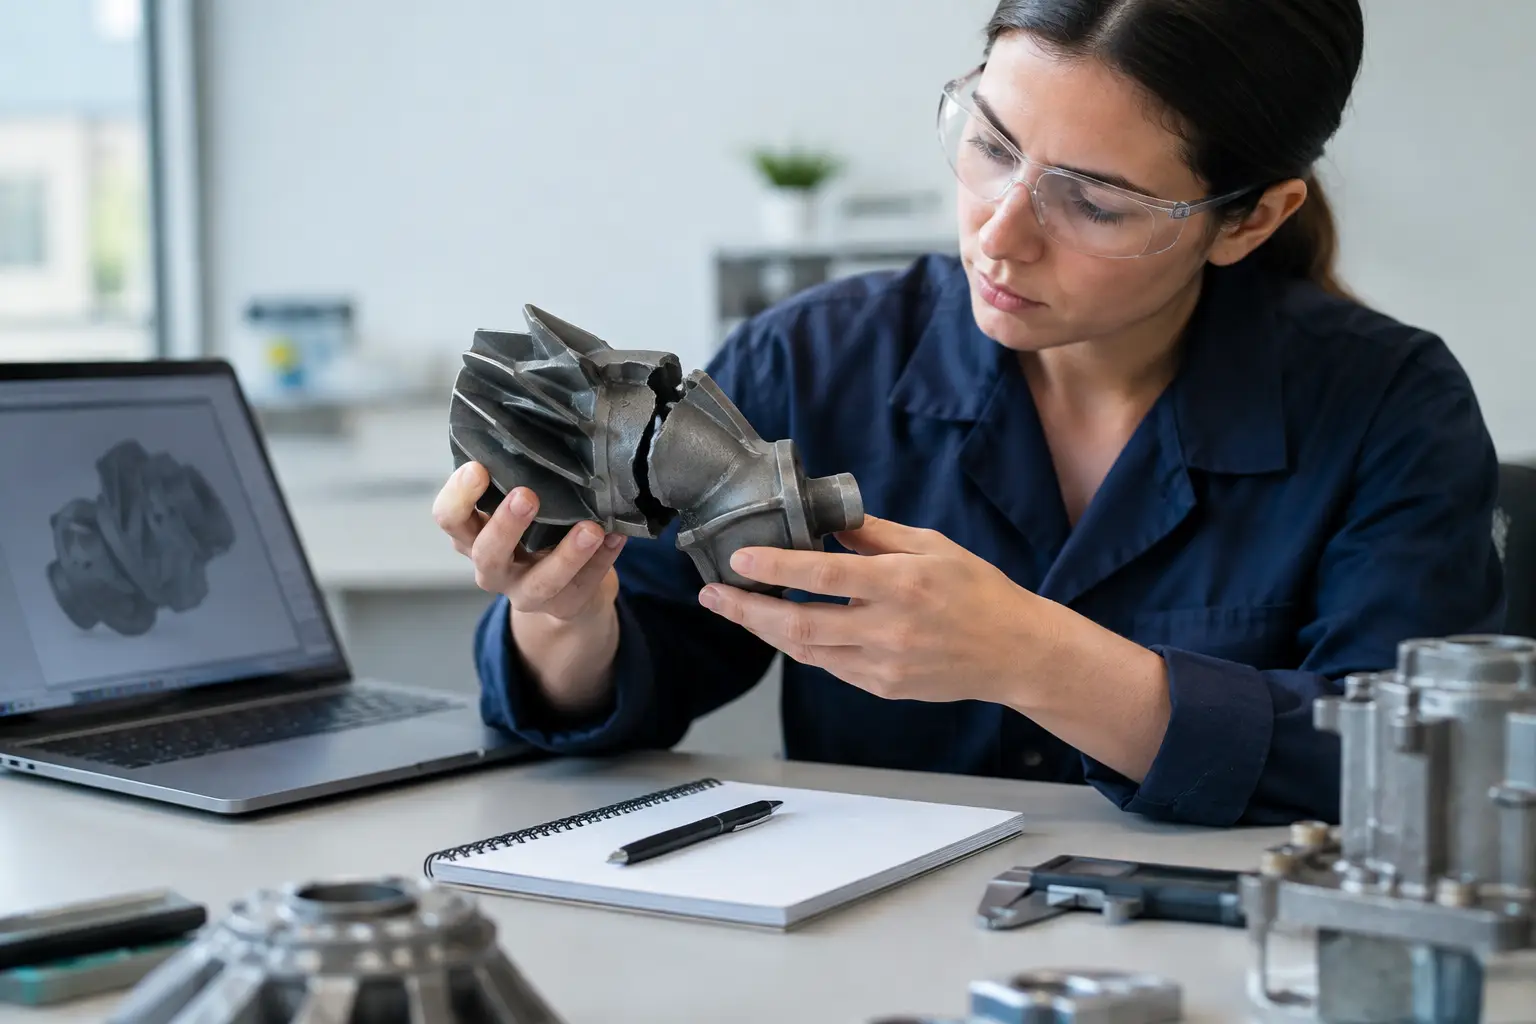
A cracked bracket, an overheated control panel, or a product returned after three weeks can all trigger the same pressure: find the person who made the mistake. Effective design failure analysis starts somewhere more useful. It asks how the system allowed the failure to occur, why existing controls did not catch it, and what change will reduce the chance of recurrence.
That distinction matters because most engineering failures are not caused by one bad drawing, calculation, or decision. They emerge from interactions between requirements, assumptions, materials, manufacturing variation, operating conditions, and communication. A useful analysis turns an incident into evidence for the next design cycle.
What Design Failure Analysis Is Actually For
Design failure analysis is the disciplined investigation of a product, component, or system that did not meet its intended function. The work may begin after a field failure, a failed qualification test, a manufacturing escape, or an issue found during a design review.
The immediate technical question might be simple: Why did this shaft fracture? But the engineering question is broader: Why was the shaft exposed to a load condition that its design, material selection, safety factor, test plan, or installation instructions did not adequately address?
A strong analysis produces more than a root-cause statement. It establishes the failure mechanism, identifies contributing factors, tests the evidence against plausible alternatives, and recommends actions that are specific enough to verify. “Improve the design” is not a corrective action. “Increase fillet radius from 0.5 mm to 2.0 mm, then validate with fatigue testing at the revised load spectrum” is.
The goal is not to prove that a design was poor. It is to make the next design decision better informed.
Begin With the Failure Definition
Teams often lose time because they begin analyzing before they have agreed on what failed. A clear failure definition sets the boundary for the investigation.
Describe the intended function, the observed behavior, the operating environment, and the impact. If a pump failed to deliver required flow, record the specified flow range, actual flow, fluid properties, pressure conditions, run time, temperature, and installation configuration. Avoid early labels such as “defective” or “underdesigned.” Those words imply a conclusion before the evidence is reviewed.
The failure definition should also separate functional failure from physical damage. A cracked housing may be the visible symptom, but the functional failure could be loss of containment, excessive vibration, or electrical exposure. This distinction helps the team focus on the consequence that matters to users and to the system.
Preserve evidence early. Retain failed units, matching control samples, packaging, installation hardware, production records, test logs, photos, and relevant software versions. A damaged part that is cleaned, reworked, or discarded before inspection can remove the best evidence of the failure mechanism.
Build a Timeline Before Naming a Cause
A timeline is one of the simplest ways to expose weak assumptions. Start with design inputs and major design changes. Add supplier changes, material lot information, manufacturing dates, inspection results, shipment, installation, operating events, maintenance activity, and the point of failure.
This sequence can reveal patterns that are invisible in a static report. For example, failures may begin after a molding tool modification, but only in units installed outdoors. That does not automatically make the tool change the root cause. It does tell the team where to look for an interaction between geometry, material behavior, and environmental exposure.
For complex products, compare failed and non-failed populations. What do they share? What differs? Useful comparison variables include lot, supplier, location, duty cycle, operator procedure, configuration, temperature, and age in service. A single failed sample can support a hypothesis. A pattern across samples can support a conclusion.
Establish the Failure Mechanism
The failure mechanism explains the physical or logical path from normal operation to failure. It should be supported by evidence, not just experience.
For mechanical components, inspection may involve fracture surface examination, dimensional measurement, hardness checks, microscopy, material verification, and load reconstruction. A fatigue fracture, for instance, has different indicators than a single overload event. Corrosion-assisted cracking, wear, creep, and manufacturing defects can create similar visible damage while requiring very different corrective actions.
Electrical and electronic failures require the same discipline. Was the component damaged by overvoltage, thermal cycling, inadequate clearance, moisture ingress, solder fatigue, firmware behavior, or an assembly error? Replacing a failed capacitor without understanding why it failed may create a short-term repair and a repeat field issue.
Analytical models and simulation are valuable when they reflect the actual condition. A finite element model based on nominal geometry and ideal constraints can miss the feature that governs real-world performance: a sharp edge, assembly preload, tolerance stack-up, or load path introduced by installation. Test results are not automatically more trustworthy either. A test can be precise and still be unrepresentative of field use.
The strongest analyses connect inspection, calculations, and testing. Each method should challenge the others.
Look Beyond the Immediate Technical Cause
A root cause is often described at the wrong level. “Material was too brittle” may be true, but it does not explain why the material was selected, accepted, or used outside its suitable range. “Operator installed the part incorrectly” may describe the final event, but it may conceal an ambiguous instruction, an inaccessible fastener, or a design that permits incorrect assembly.
This is where design failure analysis becomes a cross-functional activity. Engineering, quality, manufacturing, service, and suppliers may each hold part of the evidence. The point is not to expand the meeting. It is to examine the interfaces where assumptions commonly go untested.
A practical cause chain might look like this in prose: low-temperature impact loading caused a latch to crack; the selected resin had insufficient impact margin at the lowest service temperature; the requirement specified an ambient range but did not define impact performance at that range; qualification testing used room-temperature samples. The corrective action must address the requirement and validation gap, not only the latch material.
Use Tools Without Letting Them Replace Judgment
Methods such as fault tree analysis, fishbone diagrams, 5 Whys, failure mode and effects analysis, and design of experiments can organize thinking. They are useful when the team has evidence and a clear question. They are less useful when treated as forms to complete.
The 5 Whys method can reveal a process weakness, but it can oversimplify failures with multiple contributing conditions. Fault trees help map combinations of events, especially in safety-critical systems, but their value depends on accurate logic and input data. FMEA is strongest before failure, when it drives design choices and test planning, rather than after an issue is already known.
Choose the tool to fit the uncertainty. If the mechanism is unknown, prioritize inspection and controlled testing. If the mechanism is known but its frequency is unclear, focus on production and field data. If the failure depends on several conditions occurring together, use a structured causal model rather than a single-cause narrative.
Turn Findings Into Verifiable Changes
Corrective actions should be tied directly to findings. A change may involve geometry, material, tolerance, protective features, software limits, assembly fixtures, supplier controls, inspection methods, or user documentation. The right choice depends on where the risk can be reduced most reliably.
Design changes generally provide stronger control than training or warnings because they do not rely on perfect human behavior. Still, a redesign may introduce cost, weight, manufacturability, or performance trade-offs. Increasing wall thickness can improve strength while creating sink marks, longer cycle times, or thermal distortion. A higher-grade material may solve a durability issue while complicating supply or processing.
Verification must match the original failure. If a component failed under combined vibration and heat, a room-temperature static load test is not enough. Define acceptance criteria before testing, document deviations, and test enough samples to support the decision. For high-consequence applications, independent review may be warranted.
Close the loop by updating the artifacts that guide future work: requirements, design standards, drawings, control plans, test procedures, FMEA records, and lessons learned. A corrective action that lives only in a presentation will fade when the project team changes.
Write the Analysis So Others Can Use It
A failure report should let another engineer understand what happened without attending every discussion. State the problem, evidence, analysis methods, findings, contributing factors, corrective actions, verification results, and remaining limitations. Distinguish facts from interpretations. If a conclusion has moderate confidence because sample size is limited, say so.
Clear reporting also prevents a familiar failure mode in engineering organizations: the same issue being analyzed repeatedly by different teams. A concise, searchable record gives future designers a real starting point and gives contributors to technical communities a useful standard for sharing field experience.
The best time to learn from a failure is while the evidence is still available and the decision is still changeable. Treat the analysis as part of design work, not paperwork after the work is done.